Followed a controlled SSH authentication failure from the Ubuntu journal to a custom Wazuh alert, then tested account-specific password restrictions and removed temporary network access.
Verified achievement
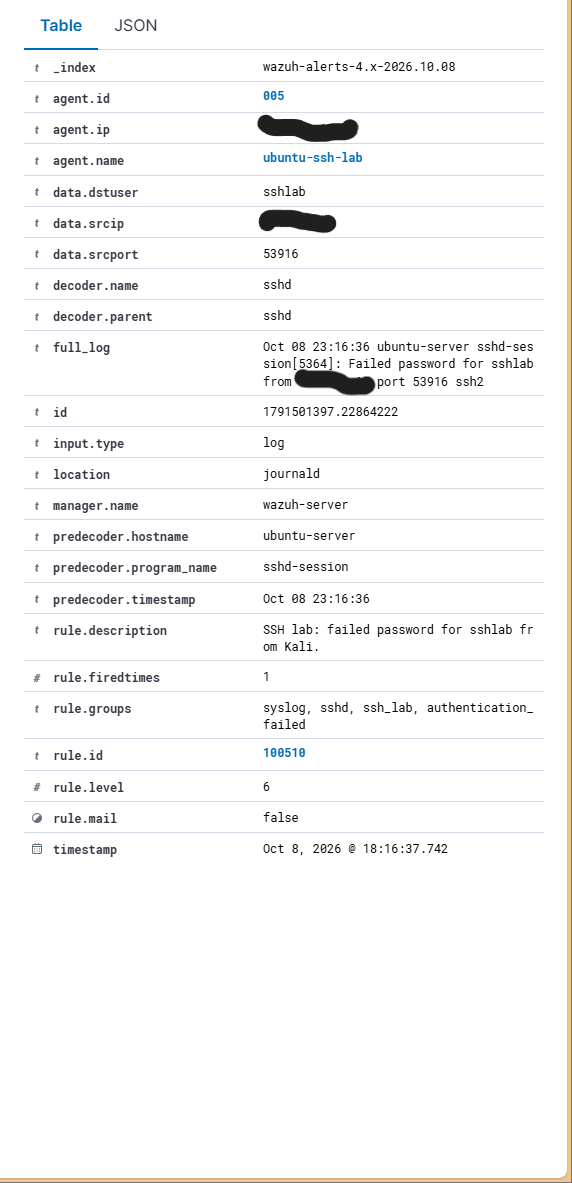
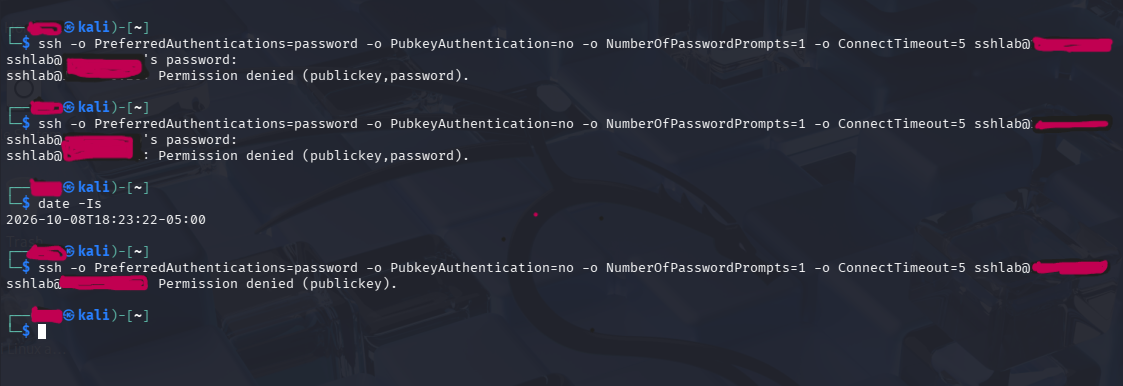
Built and validated Wazuh rule 100510, level 6 for the dedicated lab account and source. Confirmed a real event in both the manager alert file and Threat Hunting. After SSH hardening, the same password-only client command failed without a password prompt, while a fresh management login succeeded.
Lab architecture
Kali ── dedicated Proxmox test bridge ── Ubuntu test interface
                                            │
                                  management interface
                                            │
                                      Wazuh manager
The test bridge had no physical uplink, host address, or gateway. Kali had no default route. Ubuntu retained management connectivity, with IPv4 and IPv6 forwarding disabled.
Evidence and results
Stage
Observed result
Network baseline
TCP port 22 filtered before a temporary source-scoped UFW allowance, then open.
Authentication baseline
Two verified failed-password events; Wazuh rules 5760 and 5503 detected SSH and PAM failures.
Custom detection
Live rule 100510 alert verified in alerts.json and the dashboard.
Account hardening
Password and keyboard-interactive authentication disabled for sshlab.
Client verification
Password-only SSH rejected without a prompt; server recorded a preauthentication closure.
Original screenshots were cropped and manually redacted to cover network addresses and the personal terminal username. Rule details, timestamps, and test results remain visible.
Custom rule 100510, level 6, reached Threat Hunting. The dashboard alert time of 18:16:37.742 (UTC−05:00) corresponds to 23:16:37.742 UTC in the manager log.Before hardening, the password-only client command offered a password prompt. After hardening, it returned Permission denied (publickey) without a prompt. This verifies removal of the password path, not successful key authentication.
Investigation and limits
A positive rule test initially passed while a live event matched the built-in rule. Removing the hostname condition resolved the observed discrepancy after validation and restart. The exact internal cause was not established.
The final custom rule scopes by source address and account across monitored endpoints. Brute-force correlation thresholds and working key authentication were not tested. A PAM alert is not an additional independent password attempt.
The two redacted screenshots above support the custom-alert and client-behavior results. Additional server and configuration checks are documented in the technical write-up. No reconstructed evidence is used.