October 1–5, 2026 • Proxmox VE • pfSense • Wazuh SIEM/XDR • Windows Server • Active Directory • FIM • Detection Engineering • Email Alerting
Project Summary
Built, recovered, and validated a multi-VM cybersecurity lab on Proxmox VE behind a pfSense-segmented network. The project progressed from virtualization and network recovery into centralized Wazuh monitoring, Active Directory security-event validation, File Integrity Monitoring, SOC-style event correlation, privileged Domain Admins membership monitoring, custom Wazuh detection engineering, and email alert delivery.
Proxmox VEpfSenseWazuhWindows Server 2022Active DirectoryFIMPrivileged GroupsCustom RulesPostfixUbuntuKali Linux
October 1 — Proxmox Build and VM Foundation
Deployed Proxmox VE on dedicated hardware and integrated it with the isolated 192.168.10.0/24 cybersecurity lab network.
Configured the Proxmox management address as 192.168.10.80/24 with pfSense gateway 192.168.10.1.
Created and configured Ubuntu Server, Kali Linux, Wazuh Server, and Windows Server 2022 virtual machines.
Established the base architecture for Windows, Linux, SIEM, and Active Directory testing.
October 2–3 — Network Recovery and Wazuh Integration
Diagnosed a Proxmox connectivity failure where the host at 192.168.10.80 became unreachable from the Windows management system.
Verified the Proxmox route table still contained the default route through 192.168.10.1 on vmbr0.
Reviewed /etc/network/interfaces and confirmed the static bridge configuration for vmbr0.
Used bridge link show, ip addr, and interface-state checks to isolate the problem to the physical NIC / live bridge path.
Brought the physical interface back up, restored bridge connectivity, and repeatedly re-tested the gateway and Windows management endpoint.
Confirmed successful Windows-to-Proxmox ICMP testing with 0% packet loss after recovery.
Restored access to the Proxmox web interface at https://192.168.10.80:8006.
Reviewed pfSense lab addressing and static mappings during validation.
Verified Wazuh Manager, Indexer, and Dashboard services and enrolled Windows, Windows Server, Ubuntu, and Kali endpoints.
Confirmed Windows security-event collection, including failed-logon alerting from Windows Server 2022.
Troubleshooting Evidence — October 1–3
The project record includes screenshots captured throughout the recovery sequence. They document the failure state, Layer 2/Layer 3 checks, and successful recovery validation.
Microsoft Edge timeout while attempting to reach 192.168.10.80:8006.
Proxmox ip route output showing the default route via 192.168.10.1 and source address 192.168.10.80.
/etc/network/interfaces showing the static vmbr0 configuration and bridge port assignment.
Physical-interface and bridge-state troubleshooting using ip link, ip addr, and bridge link show.
Initial Destination Host Unreachable / 100% packet-loss results during diagnosis.
Successful Windows ping to 192.168.10.80 with four replies and 0% loss after recovery.
pfSense DHCP/static-mapping page showing the organized lab IP plan for infrastructure and security VMs.
Recovered Proxmox web console showing the VM inventory after connectivity was restored.
Windows File Integrity Monitoring
Configured real-time Windows File Integrity Monitoring using a dedicated test directory and verified both file creation and checksum-change activity in Wazuh.
Rule 554 — file added
Rule 550 — integrity checksum changed
MD5, SHA1, and SHA256 integrity data captured for validation.
Active Directory Security Monitoring
Windows Server 2022 was monitored as an Active Directory Domain Controller and Wazuh was used to validate key account-management and authentication events.
4624 — Successful logon
4625 — Failed logon
4720 — User account created
4722 — User account enabled
4724 — Password reset attempt
4725 — User account disabled
4726 — User account deleted
4728 — Member added to global security group
4729 — Member removed from global security group
4740 — User account locked out
4767 — User account unlocked
SOC-Style Investigation
A controlled account-lockout scenario was used to correlate repeated failed authentication attempts with the resulting lockout event.
Investigation chain: 4625 → 4625 → 4625 → 4740
Wazuh was used to review the target account, source system, timestamps, rule IDs, severity, and Windows Security event context. The activity was confirmed as authorized lab testing.
October 4 — Privileged Domain Admins Monitoring
A controlled account named PrivTest was temporarily added to the Domain Admins group and then removed. Wazuh captured both membership changes and exposed the changed member, privileged target group, administrative actor, and domain controller.
4728: PrivTest added to Domain Admins 4729: PrivTest removed from Domain Admins
Wazuh evidence — Event ID 4728, PrivTest added to Domain Admins.Wazuh evidence — Event ID 4729, PrivTest removed from Domain Admins.
October 5 — Custom Wazuh Level 14 Detection and Email Alerting
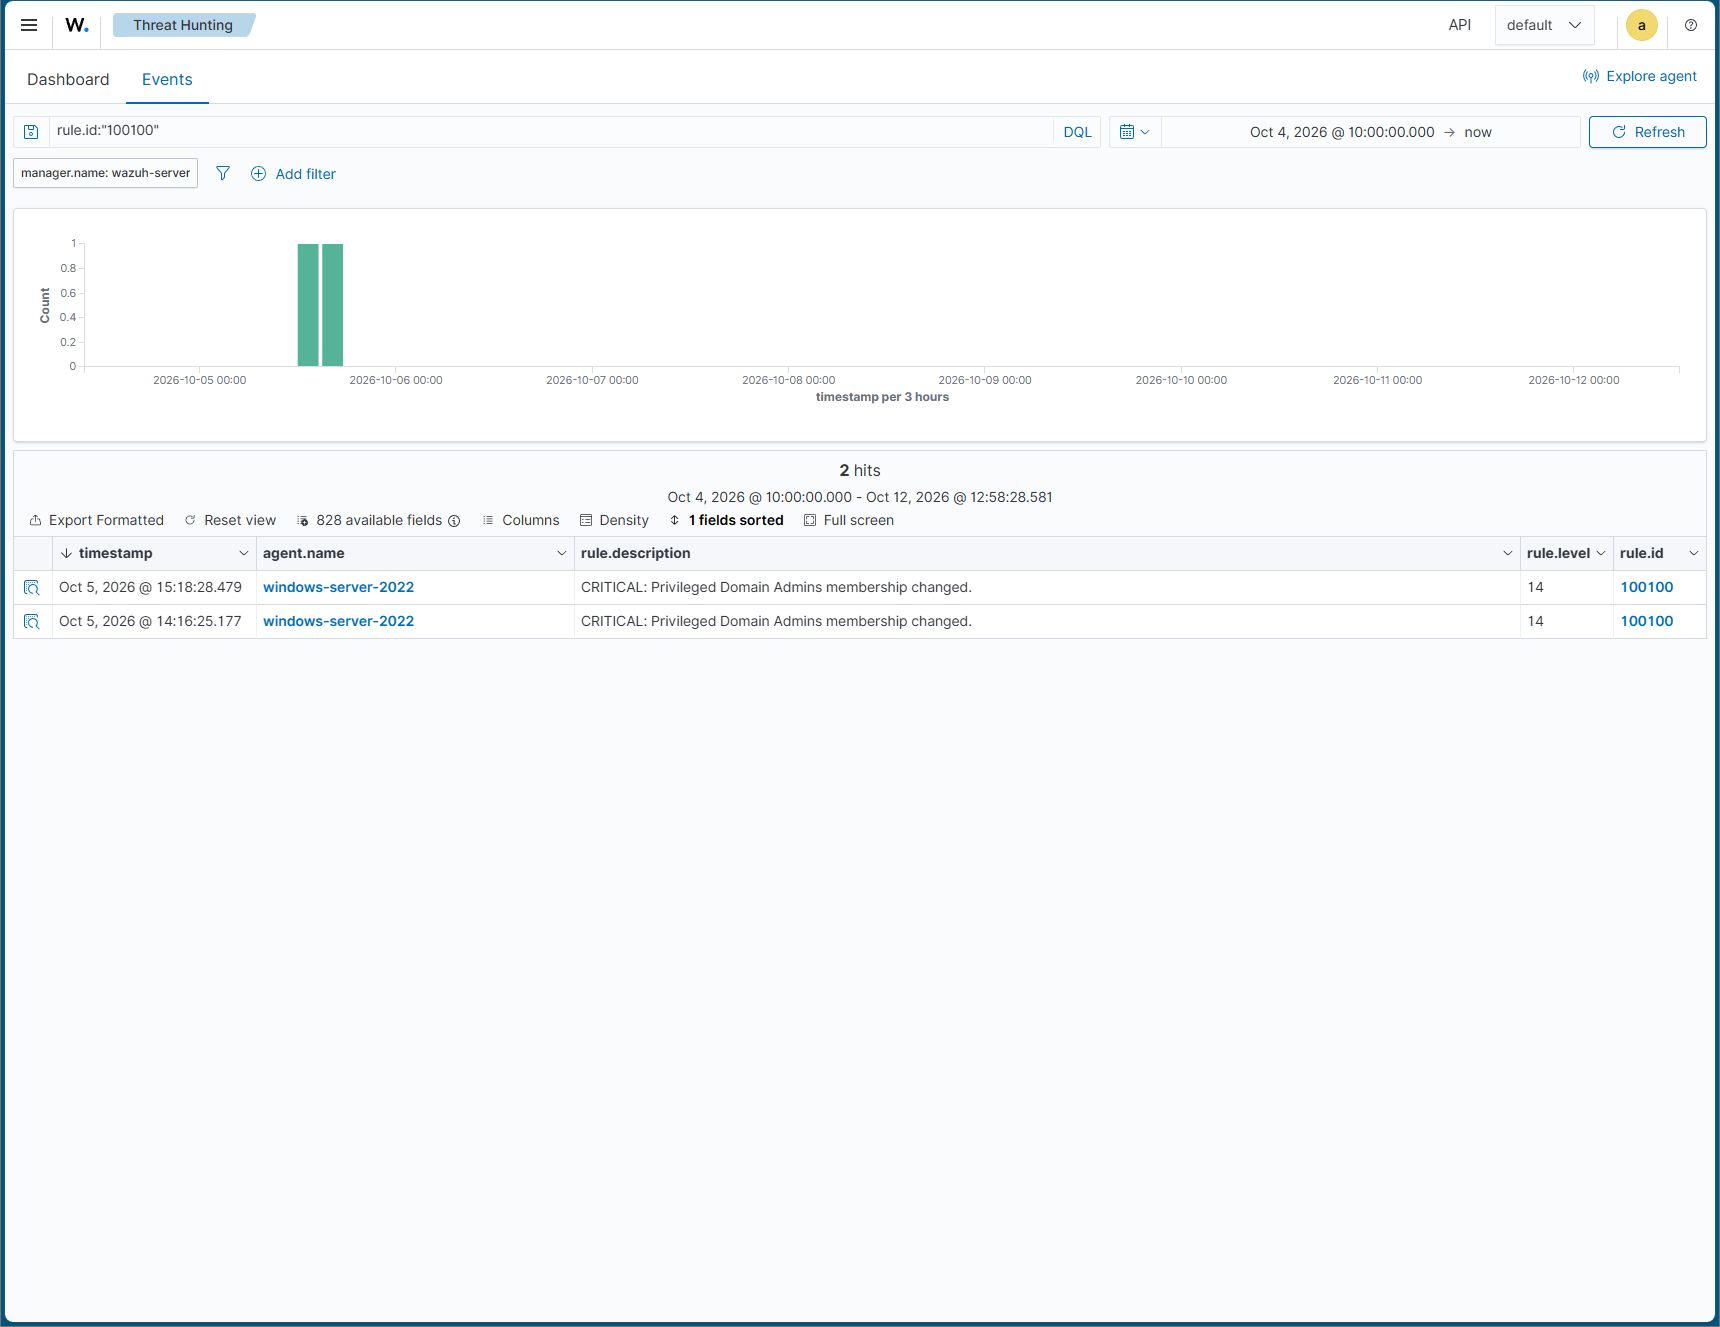
Extended the privileged-group monitoring workflow by creating a custom Wazuh child rule for Domain Admins membership changes. The custom detection was linked to built-in Wazuh rule 60159, assigned Rule ID 100100, and raised to Level 14.
Matched the Domain Admins target group using a PCRE2 field condition.
Validated the custom rule with controlled Event IDs 4728 and 4729.
Confirmed Wazuh displayed rule.id: 100100, rule.level: 14, and the description CRITICAL: Privileged Domain Admins membership changed.
Configured Postfix on the Wazuh server as a local SMTP relay.
Configured authenticated Gmail relay using TLS, SASL, Google 2-Step Verification, and a dedicated App Password.
Used mailq to diagnose an initial Gmail authentication failure and corrected the credential method.
Verified a standalone Postfix test email before enabling Wazuh notifications.
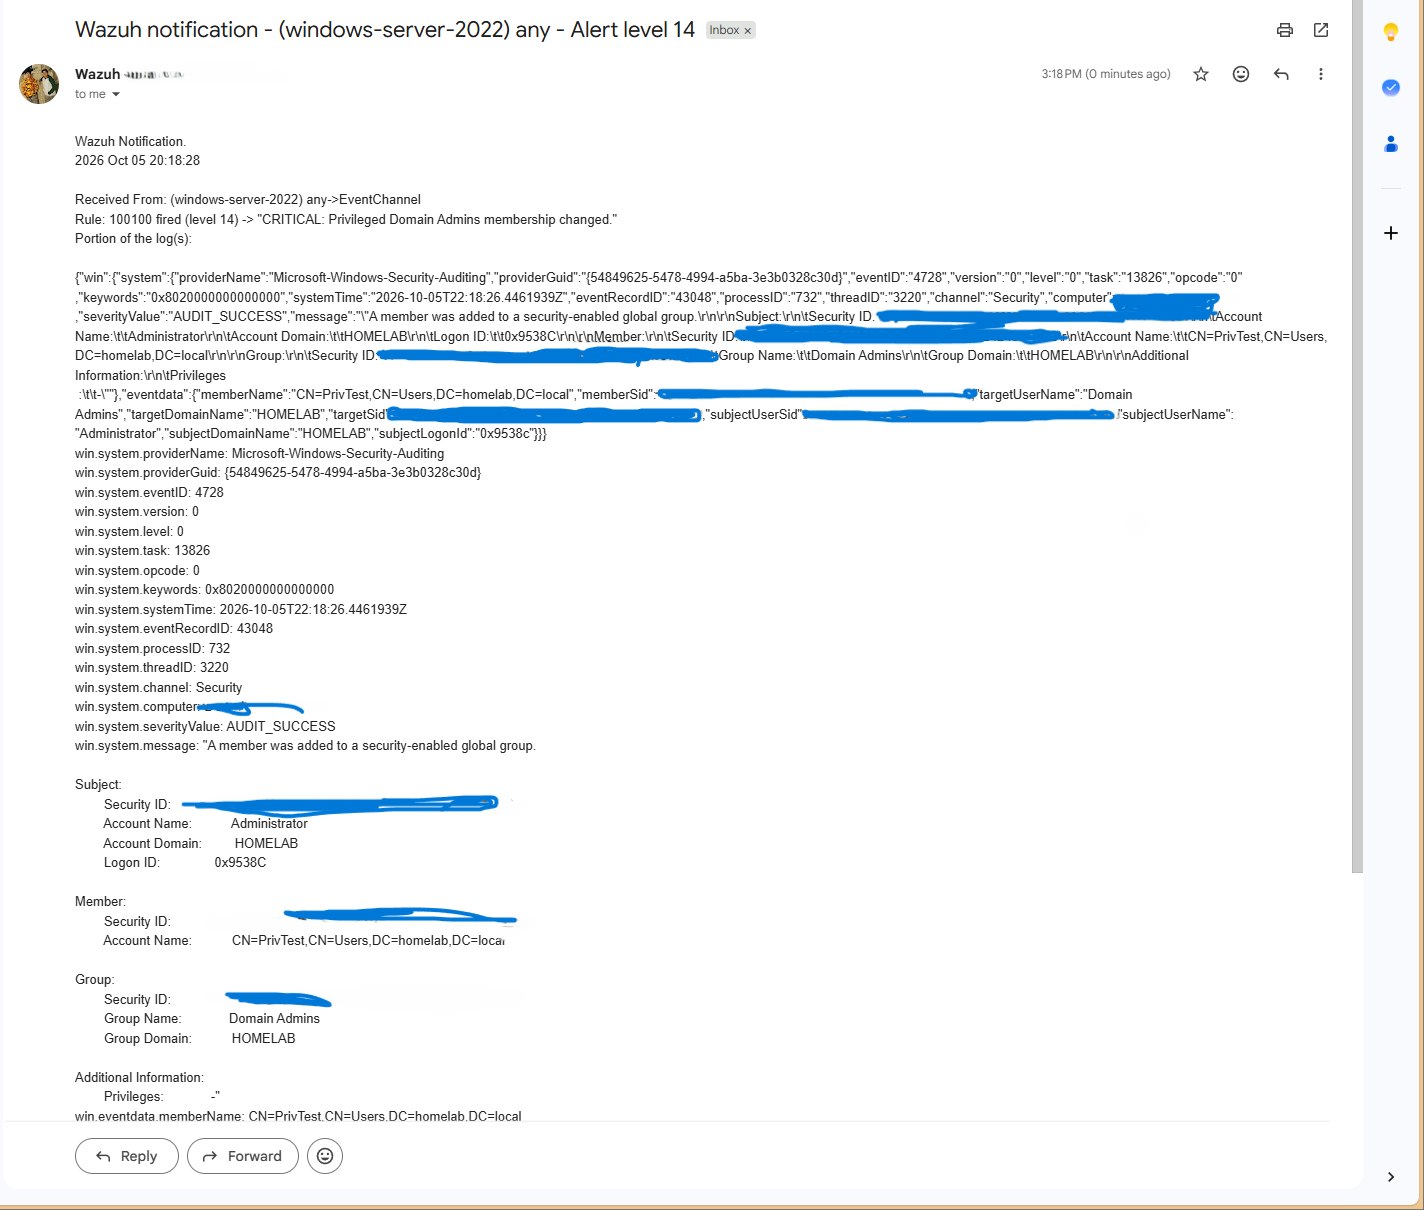
Triggered another controlled privileged-group change and received a Wazuh email containing Alert level 14, Rule 100100, Event ID 4728, and the Domain Admins context.
Successfully demonstrated privileged Active Directory monitoring
using Wazuh SIEM, including custom Rule 100100 (Level 14),
Windows Security Event ID 4728, and automated email alerting.
View the published project demonstration and supporting screenshots: